
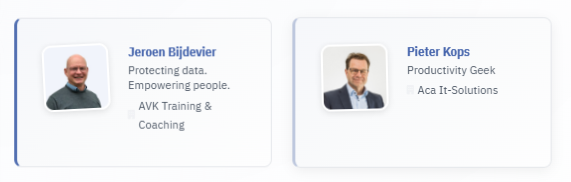
CollabDays Bletchley Park 2026 — Wednesday 23 September, 11:50–12:40, Room 1, The National Museum of Computing
Microsoft 365 Copilot does not change a single permission in your tenant. It changes what people can find. That distinction is the whole reason this session exists.
Copilot is a mirror
Every legacy SharePoint site, every overshared document, every unmanaged Team with external guests — Copilot can surface all of it, because the user already had access. Nothing new is granted. What changes is reach: one prompt now searches across everything that used to be buried five clicks deep in a forgotten library.
And Copilot cannot tell the difference between the current version of a contract and the draft that has been rotting in a project site since 2021. That ambiguity was always there. Now it answers questions with it.
So the fix is not blocking Copilot. The fix is getting the underlying data estate in order.
Three decisions before you go live at scale
In the session we work through three questions every admin has to answer:
- Which content should Copilot be able to surface?
- Which content needs to stay available, but should no longer be actively indexed?
- Which content must be retained, archived or removed according to policy?
Notice what is not on that list: blanket deletion. We do not believe in deleting content nobody dares to touch, and we do not believe in switching Copilot off by default either. Both are ways of avoiding the decision.
Step 1 — ROT: usefulness and necessity
Redundant, obsolete and trivial content is digital pollution. It accumulates silently, grows every day, and enlarges the surface Copilot retrieves from. SharePoint has a habit of growing, never shrinking.
Pieter opens with the two questions you can ask about any piece of content:
- Usefulness — is it actually still used by anyone?
- Necessity — must it be kept for a legal, regulatory, contractual or business reason?
If the answer to both is no, it is a candidate for archiving or removal. Redundant content gets consolidated to one authoritative location. Obsolete content moves to an archive or gets a retention label, so it stops being actively indexed. Trivial content is mostly a behavioural fix — people need somewhere personal to put things, not an IT project. And every item needs an accountable owner, because without one nobody ever answers those two questions.
Step 2 — SharePoint Advanced Management: inventory, urgency, action
This is where I take over, and where most tenants discover they have been guessing.
Start with the Data Access Governance reports: site permissions org-wide, permissions for a single user (if this identity were compromised, what could it reach?), and the sensitivity label report showing where labelled — and unlabelled — sensitive content actually lives. Export it, then flag the obvious: sites shared with Everyone except external users, anonymous or company-wide links, sites with no active owner.
Then tier the findings by sensitivity, breadth of access and activity. Not every finding is equally urgent, and treating them as if they are is how cleanup projects stall.
Only then act: site-level access restriction to narrow access without a full permissions overhaul, site lifecycle management for inactive sites and ownership attestation, and Restricted Content Discovery to keep content out of search and Copilot without touching permissions at all. That last one is a bridge, not a strategy — it buys you time while you fix the real problem.
The same logic applies to Restricted SharePoint Search: a curated set of sites is a fine way to start, as long as everyone understands it is temporary.
Step 3 — Records Management and archiving
Access under control? Then the question becomes how long any of this should live.
Data Lifecycle Management gives you broad, largely automated retention and deletion. Records Management adds the part you need when disposal has to be provable: a file plan, regulatory records, disposition review with an audit trail. Most organisations run both.
We also show the metadata-driven route — a site column and content type, mapped through the search schema to a RefinableString, feeding an auto-apply policy in an adaptive scope. It works well, but distribution takes days and the portal does not always tell you the truth, so verify with PowerShell rather than assuming.
Pieter closes with archiving: when to archive a whole site versus archiving at file level, how Microsoft 365 Archive works for individual documents inside active sites, and how to cut Copilot noise without deleting content people may still need.
What you take home
- Copilot is a mirror, not a cause — it surfaces governance debt that already existed.
- Start with visibility before touching permissions or retention.
- Automate where you can, review where it matters.
- This is a continuous cycle, not a one-off project.
The session is aimed at Microsoft 365 and SharePoint admins, security and compliance managers, and anyone planning a Copilot rollout on top of years of unmanaged data. You do not need to be a Purview specialist.
If you are at Bletchley Park on 23 September, come and find me afterwards — I am always curious which of the three questions above is the hardest one in your organisation.